Security & AI Governance Advisory

Adopt AI and cloud safely, without slowing your business down.

Practical security, compliance and AI governance from a former VP of Information Security, with 20+ years across SaaS, banking, logistics, critical infrastructure and defense.

CISSP CISA ISO 27001 SOC 2 PCI DSS GDPR EU AI Act NIST AI RMF

Services

Security that helps the business say yes

Most companies don't need more security tools. They need clear decisions, controls people actually follow, and evidence that satisfies customers and auditors.

AI Governance & Secure AI Adoption

Your teams are already using AI. I help you bring it into the open, with guardrails people actually follow.

  • One-page AI acceptable use policy
  • Data classification rules for AI inputs
  • AI vendor and third-party risk review
  • Alignment with GDPR, the EU AI Act, NIST AI RMF and ISO/IEC 42001

Security & Compliance Programs

Build the security program your customers and auditors expect, sized for your company and budget.

  • ISO 27001 information security management systems
  • SOC 2 and PCI DSS readiness and audit support
  • Risk assessments and executive and board reporting
  • Incident response plans and playbooks

Security Automation with AI

Remove manual, repetitive security work with governed, LLM-driven workflows.

  • Automated compliance evidence collection
  • Security alert triage workflows
  • Faster security questionnaire responses
  • Built on n8n and LLMs, with the same controls I recommend

Results

Recent client outcomes

Since 2023 I've advised six international clients in healthcare, finance and leisure.

4 of 4
clients achieved ISO 27001 certification or a SOC 2 report within 6 months
120 hrs
of manual security work removed each month through AI automation
3
AI tools approved for safe company-wide use under a new governance framework
< 4 hrs
to contain each of 3 significant security incidents

Client results are shared without names to protect confidentiality.

How I work

Small, practical steps you can build on

01 · ASSESS

Understand where you stand

A focused review of your risks, compliance obligations and the AI tools already in use.

02 · PRIORITIZE

Agree on a realistic roadmap

A plan sized to your budget that tackles the biggest risks first and supports your business goals.

03 · BUILD & HAND OVER

Implement it with your team

Policies, controls and automation put in place together and documented, so your team owns them.

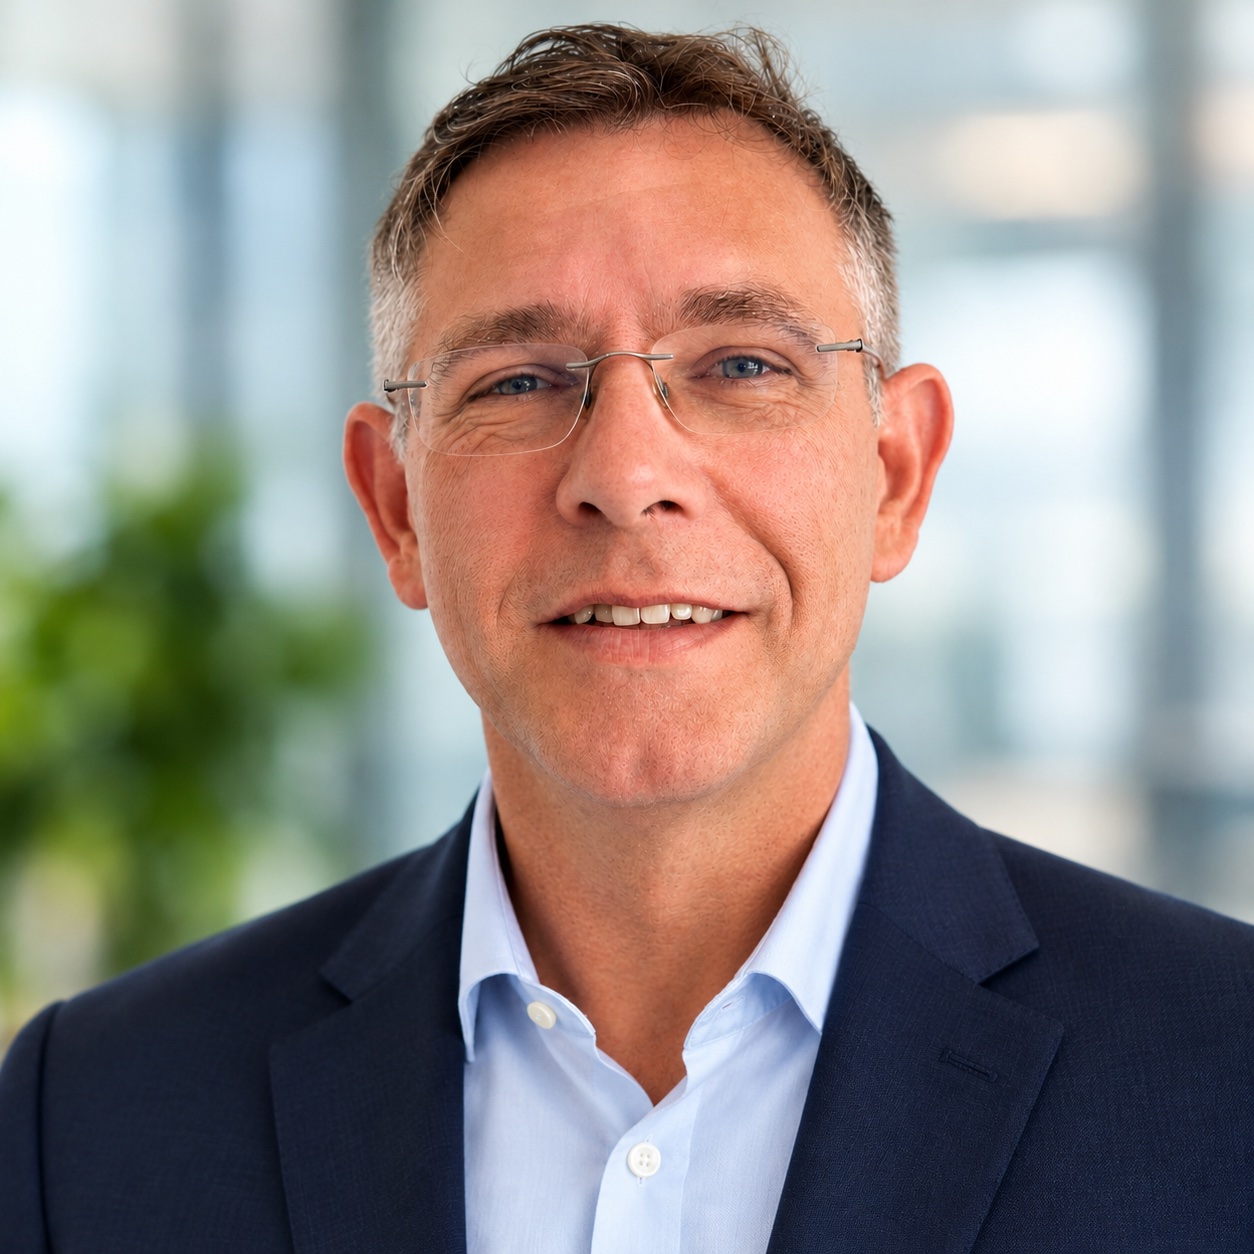
Marco de Vos

About

Hi, I'm Marco de Vos

I founded Tulp Investments LLC to help companies adopt AI and cloud safely, without slowing the business down.

I've spent more than 20 years building security programs in SaaS, banking, logistics, critical infrastructure and defense. Most recently I was VP of Information Security at Alvaria, leading a global security team across North America, Europe and India. Before that, at Aspect Software, I built the GRC function from zero and grew from Manager to Director.

Today I work directly with leadership teams on AI governance, security and compliance programs, and security automation.

  • CISSP
  • CISA
  • MSc Computer Science, University of Liverpool
  • Fluent in English, Dutch and German
View my LinkedIn profile
Insights

Latest article

Your Employees Already Use AI. Governance Should Help Them Say Yes, Safely.

A small, practical AI governance framework built on three questions, and a realistic first 90 days.

Read on LinkedIn

Contact

Let's talk

Tell me a little about your situation and what you'd like to achieve. I'll get back to you personally to set up a short, confidential call.

Thank you. Your message has been sent, and I'll be in touch soon.

Your message is delivered by email through FormSubmit. See the Privacy Policy for how your information is handled.